AI news
Two security stories landed in the same news cycle, and they describe the same shift. Attackers are no longer only breaking in — they are building pipelines that read, rank and monetise whatever they find. One story is about a ChatGPT share link that can hand an attacker far more than a single conversation. The other is about an infostealer that reportedly uses a hosted large language model to appraise the identities it steals. Neither technique is exotic. Both are cheap, and cheap is what spreads.
What actually happened
Figure: Editorial context image from the source page (preview only; rights remain with the publisher) · Credit / further reading: dev.to
The share link. ChatGPT's share feature turns a conversation into a public URL. That is a capability URL in the classic sense: possession of the link is the only credential required. The reported issue goes a step beyond casual over-sharing. A shared conversation is a rendering surface for content the model produced and for anything embedded in it — and a crafted share link can be used as the delivery mechanism in a chain that walks a victim toward exposing account-linked context or entering credentials in the wrong place. Read it as a prompt-injection and capability-URL hybrid, not a single patchable defect: the trust boundary is the render, not the endpoint.
The triage engine. Separately, a new infostealer family is described as calling out to a commercial model API to score the data it exfiltrates — not to write better malware, but to decide which compromised machines deserve human attention. Stolen browser sessions, saved cards, corporate SSO tokens and chat histories are not equally valuable. Historically, operators sorted that by hand or by crude keyword rules. An LLM turns that sort into a ranking function, and a ranking function turns a noisy haul into a prioritised target list.
The infrastructure note. The same roundup mentions that the PostgreSQL 19 cycle has slipped. It is a small item next to the first two, but it belongs in the same brief: mature projects trade schedule for safety more often than outsiders expect, and that trade is worth noticing when your own roadmap depends on their dates.
Why the share-link class is an architecture problem
Most teams already treat user input as untrusted. Far fewer treat model output as untrusted, and almost nobody treats model output that has been round-tripped through a share link and re-ingested somewhere else as untrusted. That is the gap.
Consider the ordinary path of a shared conversation inside a company: someone pastes the link into Slack, a colleague opens it, screenshots it, pastes the transcript into a ticket, and later a support bot or an internal assistant reads that ticket as context. At every hop, text that a stranger could have influenced is being read by a system that is inclined to follow instructions. The dangerous instruction does not need to be visible to a human reviewer — it only needs to survive into a context window.
The mitigations are unglamorous but effective. Neutralise rendered content rather than trusting the renderer. Treat shared conversations as public by default in your own documentation and your own UI copy. Scope any token that can reach a shared artefact down to read-only and short-lived. Rate-limit and monitor share endpoints for enumeration patterns, because capability URLs leak by design — through referrers, through archived snapshots, through a forwarded email.
Malware that triages
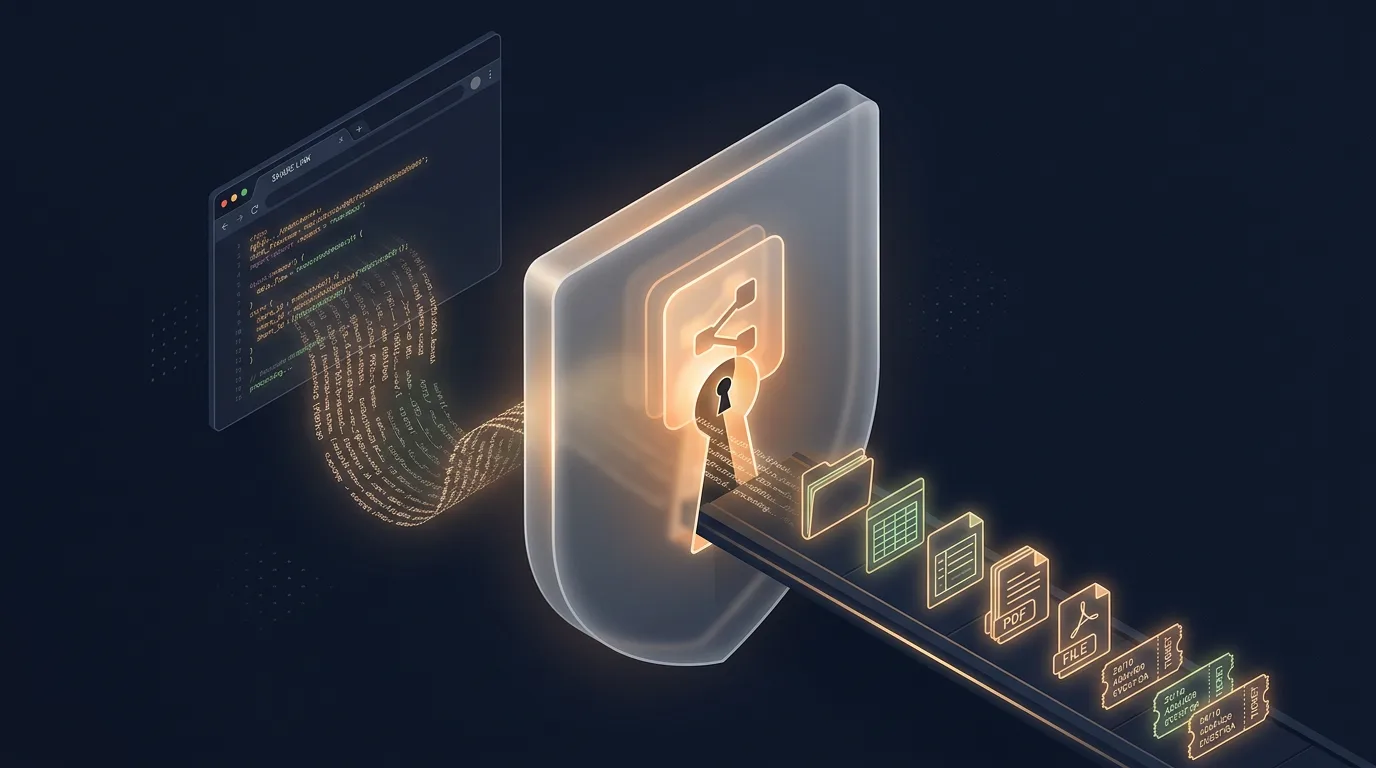
Figure: HEXOPS original illustration inspired by the topic (not a copy of the source article imagery) · Credit / further reading: dev.to
The triage story matters less for what it says about criminal sophistication and more for what it does to defence economics. When attackers can rank targets automatically, the defender's advantage of "there is too much data for them to sort" disappears. Three consequences follow.
First, incident response gets inverted. The machine you hear about first may not be the machine that matters. Asset criticality and identity value need to be part of your detection logic, not a spreadsheet consulted on day three.
Second, endpoint telemetry has to include outbound traffic to model providers. A process making small, regular calls to an inference API with a payload of local artefacts is a signal worth alerting on — and it is a signal many EDR configurations do not look for, because until recently it looked like normal developer behaviour.
Third, the leaked-data blast radius of a single laptop goes up. If an assistant can read what was stolen and rank it, then secrets that were merely present on the machine — API keys in a dotfile, a signed-in admin console, a saved recovery code — become part of the valuation rather than incidental.
What to watch next
- Whether platform vendors treat shared-conversation links with the same scrutiny as public document links: expiry, revocation, viewer analytics, and a clear default.
- Whether model providers ship provenance signals that let a downstream system tell “content the user typed” from “content the model generated and a stranger linked to.
- Whether EDR and network vendors normalise inference-API egress as a first-class category rather than an unknown SaaS endpoint.
- Whether the PostgreSQL 19 slip moves once more, which would push a lot of dependency upgrades into the same quarter.
Key takeaways
- A ChatGPT share link is a capability URL, and capability URLs leak through ordinary collaboration habits — Slack, tickets, screenshots, archives.
- The failure mode is a chain, not a single bug: injected text plus a rendered link plus a downstream system that follows instructions.
- Model output should be treated as untrusted input everywhere it is re-ingested, especially in support and internal-assistant pipelines.
- LLM-assisted triage of stolen data raises the value of every secret present on a machine, not only the ones that were the target.
- Outbound calls to inference APIs from endpoints are now a detection opportunity that most stacks ignore.
Next steps
- Inventory every place a shared conversation can be re-ingested — ticketing, chatops, RAG indices, support bots — and mark it as untrusted in your data-flow diagram.
- Add expiry and revocation to any internal feature that generates a public link, and log opens.
- Audit your endpoint detection rules for egress to model provider endpoints; add one alert this week.
- Re-rank your incident response playbook by identity value, not by alert order.
- Re-read your dependency calendar against slips like the PostgreSQL 19 cycle before you commit to a release date.